Disclosure: VPNFin is reader-supported. If you buy a VPN through links on this page, we may earn a commission at no extra cost to you. This never affects our ratings — here’s our full disclosure.
AES-256 vs ChaCha20: which VPN encryption is better? Neither is stronger. Both are 256-bit ciphers with no known practical break, and current cryptographic analysis rates them as equally secure, Encapsulated explains. The difference is speed on your hardware: AES-256 runs fastest on chips with built-in AES instructions, which most modern computers and phones have, while ChaCha20 is faster in pure software on devices without them. Our guide to VPN Encryption covers ciphers, key exchange and post-quantum protection.
In practice, your VPN protocol makes the choice for you. WireGuard, and NordLynx built on it, use ChaCha20 only; OpenVPN and IKEv2 commonly use AES-256. This page explains the trade-offs.
AES-256 vs ChaCha20: At a Glance
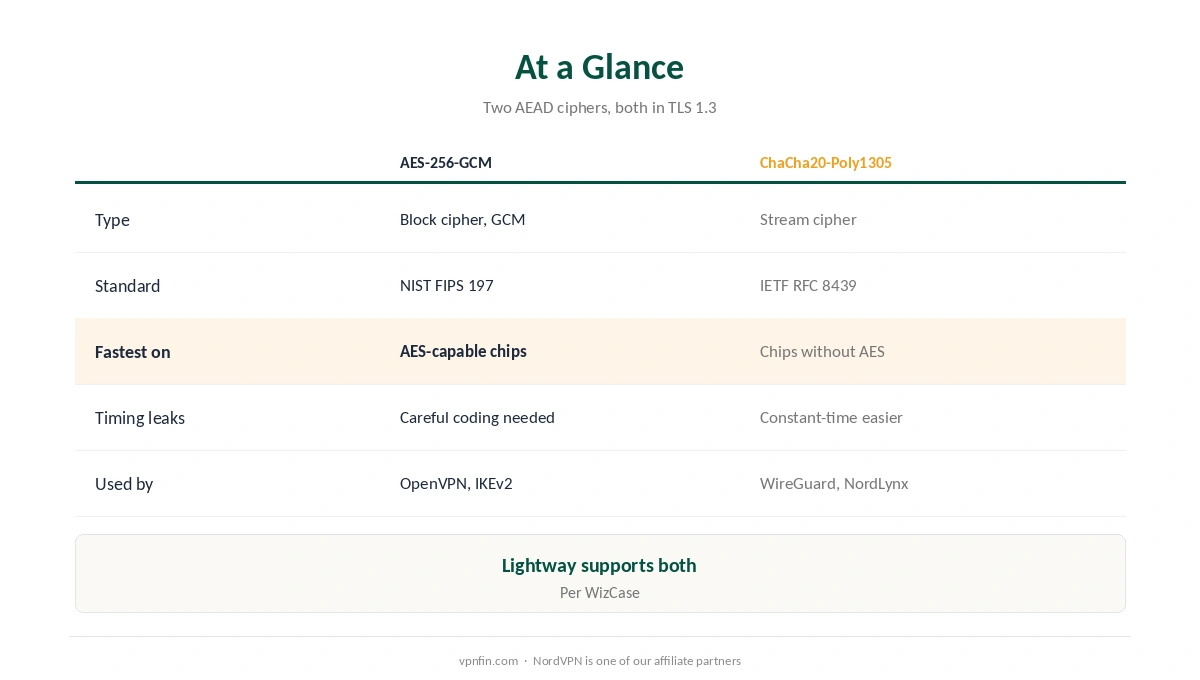
| AES-256-GCM | ChaCha20-Poly1305 | |
|---|---|---|
| Type | Block cipher (GCM mode) | Stream cipher with Poly1305 |
| Standard | NIST (FIPS 197; GCM in SP 800-38D) | IETF RFC 8439 |
| Fastest on | Chips with AES instructions | Chips without them |
| Timing leaks | Needs careful implementation | Easier to make constant-time |
| Used by | OpenVPN, IKEv2, Lightway | WireGuard, NordLynx, Lightway |
| Known practical break | None | None |
Both authenticate as well as encrypt. Each is an AEAD construction, meaning tampering with the data is detected, and both appear in TLS 1.3, the protocol behind secure websites, ZeyroVault notes.
Speed: It Depends on the Chip
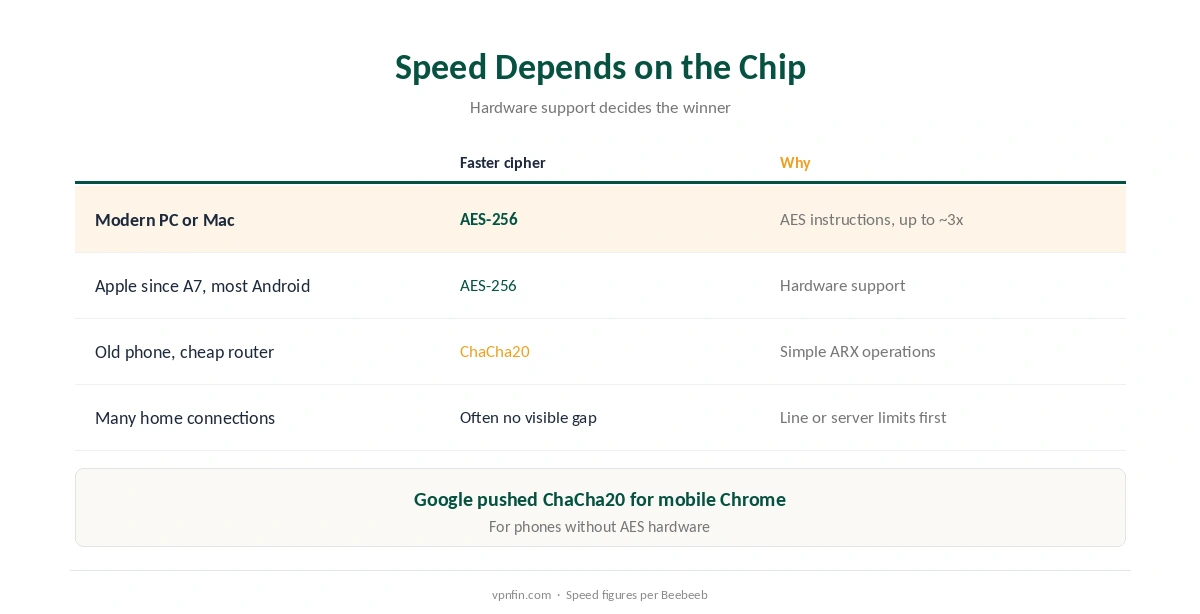
With AES hardware, therefore, AES-256 wins. On processors with AES instructions, AES-256-GCM can run up to about three times faster than ChaCha20, including on Apple’s M-series chips, Beebeeb reports. Every Apple chip since the A7 and most modern Android chips include such instructions.
Without it, by contrast, ChaCha20 wins. ChaCha20 uses only additions, rotations and XORs, which run quickly on any processor, so older phones, cheap routers and small boards often do better with it. That’s why Google pushed ChaCha20 for mobile Chrome, vpn.how notes. Phones and routers are where the choice shows most.
For many users, however, the gap is invisible, because the internet line or the server tends to limit speed before the cipher does, as our speed guide explains.
Security: A Draw
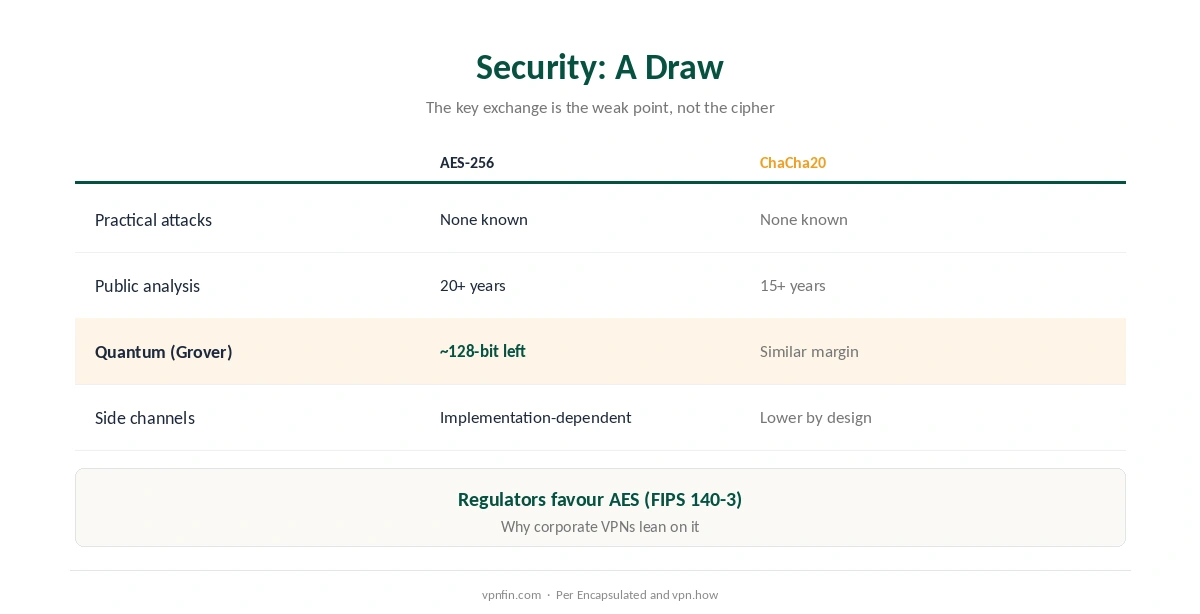
| Question | AES-256 | ChaCha20 |
|---|---|---|
| Practical attacks today | None known | None known |
| Years of public analysis | Over 20 | Over 15 |
| Quantum computers (Grover) | About 128-bit strength left | Similar margin |
| Side-channel risk | Depends on implementation | Lower by design |
Quantum computers don’t change the answer. Grover’s algorithm roughly halves the effective key strength, leaving AES-256 with around 128 bits, still a large margin; the weak point is the key exchange, not the cipher, Encapsulated explains. Our post-quantum VPN guide covers that part.
That said, regulators prefer AES. Government and banking certifications such as FIPS 140-3 are built around AES, vpn.how notes, which is why corporate VPNs lean on it.
Which Should You Use?
In short, let the protocol decide. WireGuard-based protocols use ChaCha20, and OpenVPN offers AES-256 by default. ExpressVPN’s Lightway supports both, as our Lightway vs WireGuard guide explains.
Pick the protocol for other reasons: speed, network compatibility and features, as our NordLynx guide and our privacy VPN guide cover. Either cipher protects your data equally well.
What the VPN logs matters far more than the cipher, as our audit tracker shows. New to the topic? Start with what a VPN is.
Which Protocols Use Which Cipher
WireGuard uses ChaCha20 for encryption, which is why NordLynx, built on WireGuard, does too. OpenVPN and IKEv2 typically use AES-256. ExpressVPN’s Lightway can use either, depending on the device.
You rarely choose the cipher directly. You choose the protocol, and the cipher follows. Our IKEv2 vs WireGuard guide explains the protocol side.
What Matters More Than the Cipher
Both ciphers are considered secure, so other choices decide your privacy. An audited no-logs policy matters more than the cipher; our table counts six audits for NordVPN and five for Proton VPN. A working kill switch and leak protection matter too.
Test for leaks after setup with our DNS leak guide and IPv6 leak guide. A strong cipher does not help if requests leave the tunnel.
Older Devices and Routers
Older phones and many routers lack hardware support for AES, so ChaCha20 often runs faster on them. Newer laptops and phones usually accelerate AES, which narrows the gap. If a router struggles, WireGuard is usually the better choice for that reason.
How to Pick in Practice
Choose the protocol your provider recommends for your device, then test it. On a modern laptop or phone, any default is fine. On an older Android phone or a router, try WireGuard first, since ChaCha20 suits hardware without AES acceleration. If speed disappoints, switch protocol and repeat the test at the same time of day. Keep the setting that stays steady across networks.
A Quick Rule
Modern laptop or phone? Either cipher is fine. Older Android phone or router? WireGuard with ChaCha20 often runs faster. Worried about privacy? Look at the provider’s audits rather than the cipher. Then test for leaks, because a leak undoes any cipher.
How We Research
The security comparison, WireGuard’s cipher and quantum effects come from Encapsulated; speed figures and ChaCha20’s design from Beebeeb; standards from ZeyroVault; regulatory preference and history from vpn.how. ChaCha20-Poly1305’s standard is RFC 8439. We read all sources on 28 September 2026. NordVPN is one of our affiliate partners. Our full approach lives on the About Us page.
AES-256 vs ChaCha20 FAQ
No. Both are 256-bit ciphers with no known practical break, and cryptographers rate them as equally secure.
AES-256 on chips with AES instructions, which most modern devices have. ChaCha20 on chips without them.
ChaCha20-Poly1305 only. NordLynx, built on WireGuard, uses it too.
Not in a practical sense. Grover’s algorithm roughly halves their strength, leaving a large margin. The key exchange is the part at risk.
Indirectly, by choosing the protocol. WireGuard means ChaCha20; OpenVPN typically means AES-256.
The Verdict
AES-256 vs ChaCha20 is a speed question, not a security one. Both are strong.
AES-256 wins on hardware with AES support; ChaCha20 wins without it. Choose your VPN protocol for everything else, and the cipher follows.