
Disclosure: VPNFin is reader-supported. If you buy a VPN through links on this page, we may earn a commission at no extra cost to you. This never affects our ratings — here’s our full disclosure.
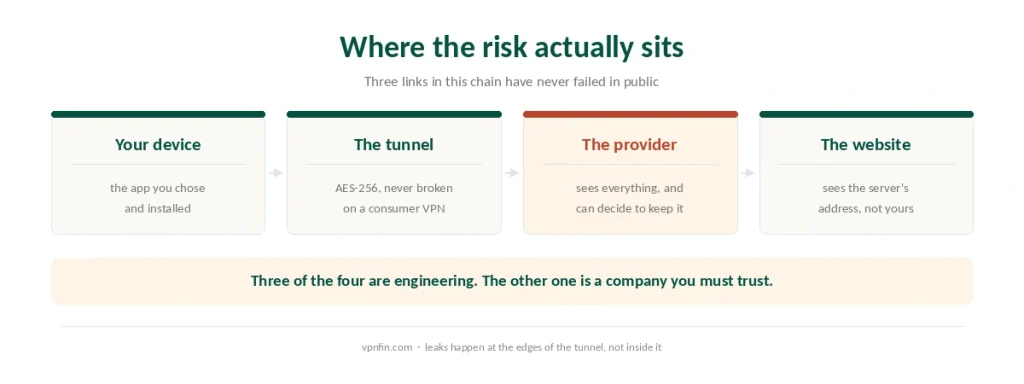
People asking whether VPNs are safe are usually asking about the encryption. That is the part nobody has broken.
The failures have all been at the other end. Companies that left databases open, kept logs while advertising none, or handed records to investigators. The tunnel held every time; the business behind it did not.
The Short Answer
The technology is safe. AES-256 and modern protocols are the same standards banks and governments rely on, and there is no public case of anyone breaking them in a consumer VPN.
The provider is the risk. A VPN moves who can see your traffic rather than hiding it, so the company at the far end sees everything your internet provider used to.
Free services are where this goes wrong most often, and the documented cases are worse than most people expect.
The Encryption Is Not the Problem
Worth dismissing properly, because it absorbs most of the worry.
AES-256 is the standard your browser already uses. Every serious provider runs it, and no consumer VPN has had its encryption broken in public.
Protocols are mature. WireGuard, OpenVPN and the vendor variants built on them have been audited repeatedly, and the known weaknesses are configuration errors rather than cryptographic ones.
⚠️ The realistic technical risk is a leak, not a break. DNS queries escaping the tunnel, WebRTC exposing your address in the browser, or a kill switch that does not fire — all three are testable in about five minutes.
The Provider Is the Problem
Here is where the actual history sits.
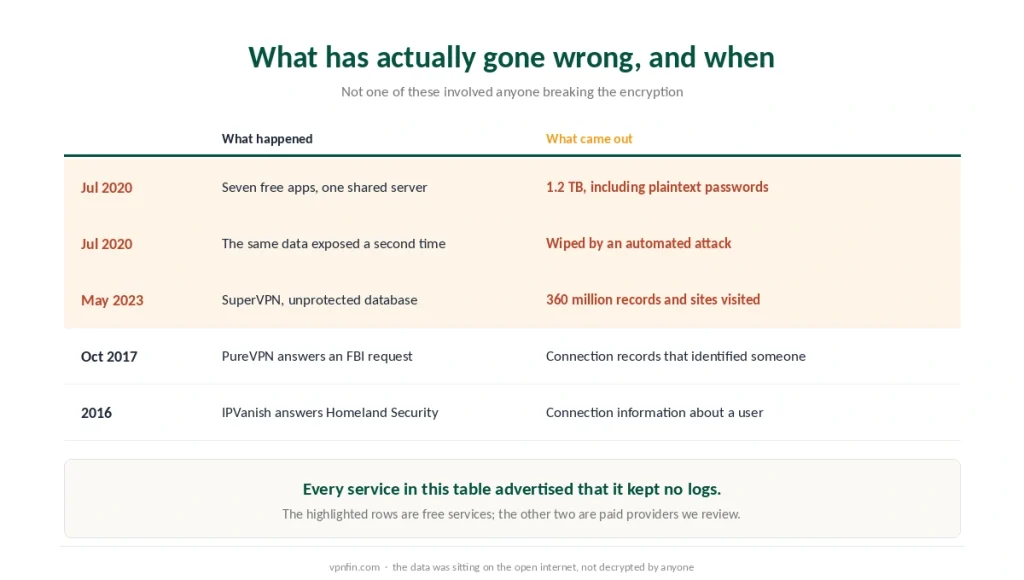
Two providers we review handed data to investigators. PureVPN supplied connection records to the FBI in 2017; IPVanish provided connection information to Homeland Security in 2016 — both incidents, and the four providers that had nothing to hand over.
Both advertised no logs at the time. That is the point: the claim is easy to make and hard to check, which is why an audit and a court record are worth more than a homepage badge.
⚠️ Ownership belongs in this calculation too. Two corporate groups hold most of the large brands, and four parents also own the sites reviewing them. A service is only as trustworthy as the company that can change its policy tomorrow.
What Actually Happened to Free VPN Users
Two incidents, both documented, both involving services marketed as private.
July 2020: seven apps, one server, 1.2 terabytes. UFO VPN, Fast VPN, Free VPN, Super VPN, Flash VPN, Secure VPN and Rabbit VPN presented themselves as separate companies while sharing a developer and an unprotected database. The exposed data included email addresses, plaintext passwords, home addresses, device identifiers and activity logs. Every one of them advertised a zero-log policy.
UFO VPN’s response is worth quoting for tone. The company attributed the exposure to personnel changes during the pandemic and said the firewall rules had since been fixed. It claimed twenty million users, and the database was recording more than twenty million logs a day.
May 2023: SuperVPN, 360 million records. A researcher found an unprotected database of 133 gigabytes containing email addresses, original IP addresses, geolocation, unique identifiers, device models and references to sites users had visited. The app had over a hundred million downloads and listed different developers on the two app stores.
December 2025: Urban VPN, eight AI assistants. Researchers reported that a browser extension with millions of users had been capturing prompts and replies from ChatGPT, Claude, Gemini and five others since a silent update in July, and sending them to an affiliated data broker — the full account has its own page.
⚠️ None of the three involved anybody breaking encryption. In every case the data was collected deliberately, by services that had promised not to collect it — which is why our free VPN guide reaches an uncomfortable conclusion. Nor does encryption stop malware, which is a different product entirely and often mis-sold as part of the same one.
How to Tell a Safe One
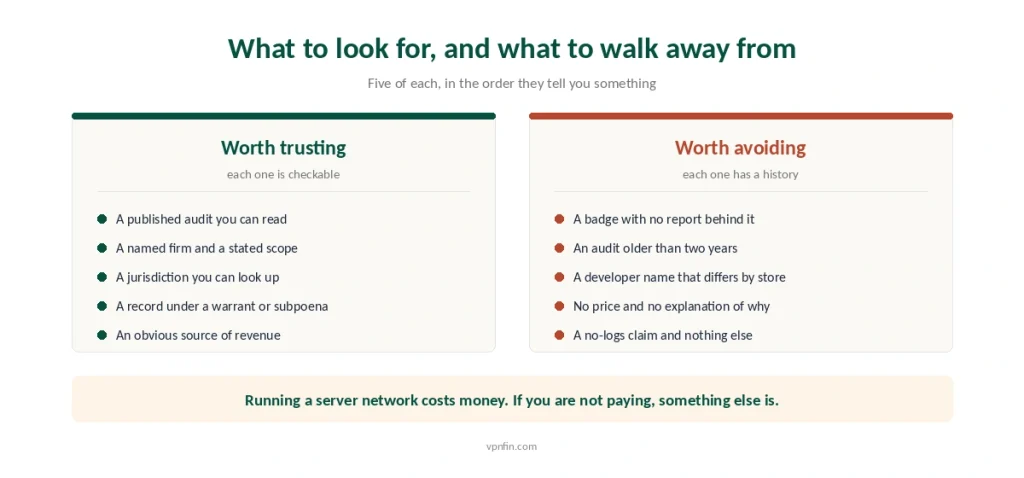
Five checks, in the order they tell you something.
A published audit you can read, with a named firm and a stated scope, dated within the last two years.
A jurisdiction you can look up. Proton VPN is Swiss, Mullvad is Swedish and owned by its founders, and both publish where they stand.
A record under pressure, if one exists. A police warrant or a subpoena that produced nothing is evidence no audit can manufacture.
A parent company you know about. If a brand belongs to a group that also owns three rivals and a review site, that is worth knowing before you read the rankings.
A price. Running a server network costs money, and a service with no subscription revenue is being funded some other way.
| Provider | No-logs audits | Auditor | Jurisdiction |
|---|---|---|---|
| NordVPN | 6 | PwC, Deloitte | Panama |
| Surfshark | 2 | Deloitte | Netherlands (9 Eyes) |
| ExpressVPN | 3 | KPMG | British Virgin Islands, Kape-owned |
| CyberGhost | 3 | Deloitte | Romania, Kape-owned |
| PureVPN | 4 | KPMG | BVI, operated from Pakistan |
| IPVanish | 2 | Leviathan, Schellman | United States (Five Eyes), Ziff Davis-owned |
| Windscribe | 1 | Packetlabs, production infrastructure | Canada (Five Eyes); Greek case dismissed, no data to give |
| Proton VPN | 5 | Securitum | Switzerland, moving infrastructure to EU |
| Private Internet Access | 3 | Deloitte | United States (Five Eyes), Kape-owned |
| Mullvad | 10+ | Cure53, Assured AB | Sweden (14 Eyes) |
| TunnelBear | Annual since 2017 | Cure53 | Canada (Five Eyes), US parent |
| Norton VPN | 2 | VerSprite | United States (Five Eyes) |
| Hotspot Shield | 0 | protocol audited, policy not | United States (Five Eyes) |
| AirVPN | 0 | none — the client is open source instead | Italy (14 Eyes) |
| IVPN | 8, annual since inception | Cure53 | Gibraltar (status disputed) |
| Hide.me | 1 modern, in 2024 | Securitum, though one source names Altius IT | Malaysia (outside the alliances) |
| PrivadoVPN | 0 | none in six years of operation | Iceland (moved from Switzerland, 2026) |
| TorGuard | 0 | none; settled a lawsuit without disclosing records | United States (Five Eyes) |
| FastestVPN | 1, in 2023 | Altius IT | Cayman Islands (outside the alliances) |
| StrongVPN | 0 | none in over two decades | United States (Five Eyes), Ziff Davis-owned |
| VyprVPN | 1, in 2018 | Leviathan Security, before the 2023 sale | United States (Five Eyes), Certida-owned since 2023 |
| PrivateVPN | 0 | none; support says there is nothing to audit | Sweden (14 Eyes), ownership disputed |
| ZoogVPN | 0 | none; support describes one as planned | Greece (outside the alliances), run from Ukraine |
The Risks That Are Overstated
Three worries that come up constantly and deserve less weight.
“Someone will intercept my VPN traffic.” No public case exists. The encryption is not where this fails.
“A VPN will get me hacked.” A reputable app is no more dangerous than any other software from a company you chose. A counterfeit app from a search advert is a different matter entirely.
“Using one is suspicious.” It is lawful almost everywhere, and businesses run them by default.
⚠️ The underrated one is what a VPN never claimed to do. It does not stop tracking, does not clean an infected device and does not make you anonymous — the full list is short and worth reading.
How We Research
This guide draws on Comparitech’s investigation of the July 2020 exposure affecting seven Hong Kong-based services, on reporting by Hackread, Fox News and vpnMentor of the SuperVPN database found in May 2023, and on our own pages for the audit records, court cases and ownership structures referenced here. Two of those outlets are owned by companies that sell VPNs — Comparitech by Point Wild, which owns Hotspot Shield, and vpnMentor by Kape — so we used them for the factual detail of incidents they researched first-hand and weighted their conclusions accordingly. We do not run our own tests. Our method lives on the About Us page.
VPN Safety FAQ
The encryption is. AES-256 and modern protocols are the same standards used by banks, and no consumer VPN has had its cryptography broken publicly. The risk sits with the provider, which sees everything your internet company used to see, and several have handled that badly.
Repeatedly. In July 2020 seven Hong Kong-based free services sharing one developer exposed 1.2 terabytes including plaintext passwords, despite advertising zero logs. In May 2023 a researcher found 360 million SuperVPN records, including original IP addresses and sites visited, on an unprotected database.
The documented incidents cluster there, and the reason is structural: running servers costs money, so a service with no subscription revenue funds itself some other way. A few reputable providers offer genuine free tiers paid for by their subscribers, which is a different arrangement entirely.
No public case exists of anyone breaking the encryption on a consumer VPN. The realistic technical failures are leaks rather than breaks: DNS queries escaping the tunnel, WebRTC exposing your address through the browser, or a kill switch that does not fire when the connection drops.
Look for a published audit with a named firm and a recent date, a jurisdiction you can verify, any record of being tested by a court or a police warrant, and the identity of the parent company. Then check that the business has an obvious source of revenue.
The Verdict
The encryption is safe and has never been the issue. No public case exists of anyone breaking a consumer VPN’s cryptography.
The company is the risk, and the record proves it. Databases left open, logs kept despite the claim, and records handed over when asked.
So the question is not whether VPNs are safe. It is whether the specific company you are about to trust has ever been checked by somebody who did not work for it.